Hi, I am Roman Smal.Ambitious.Strategic.Intelligent.
I transform ideas into results through deep analysis and relentless execution, using every challenge to push boundaries and raise the bar.
Get to Know Me
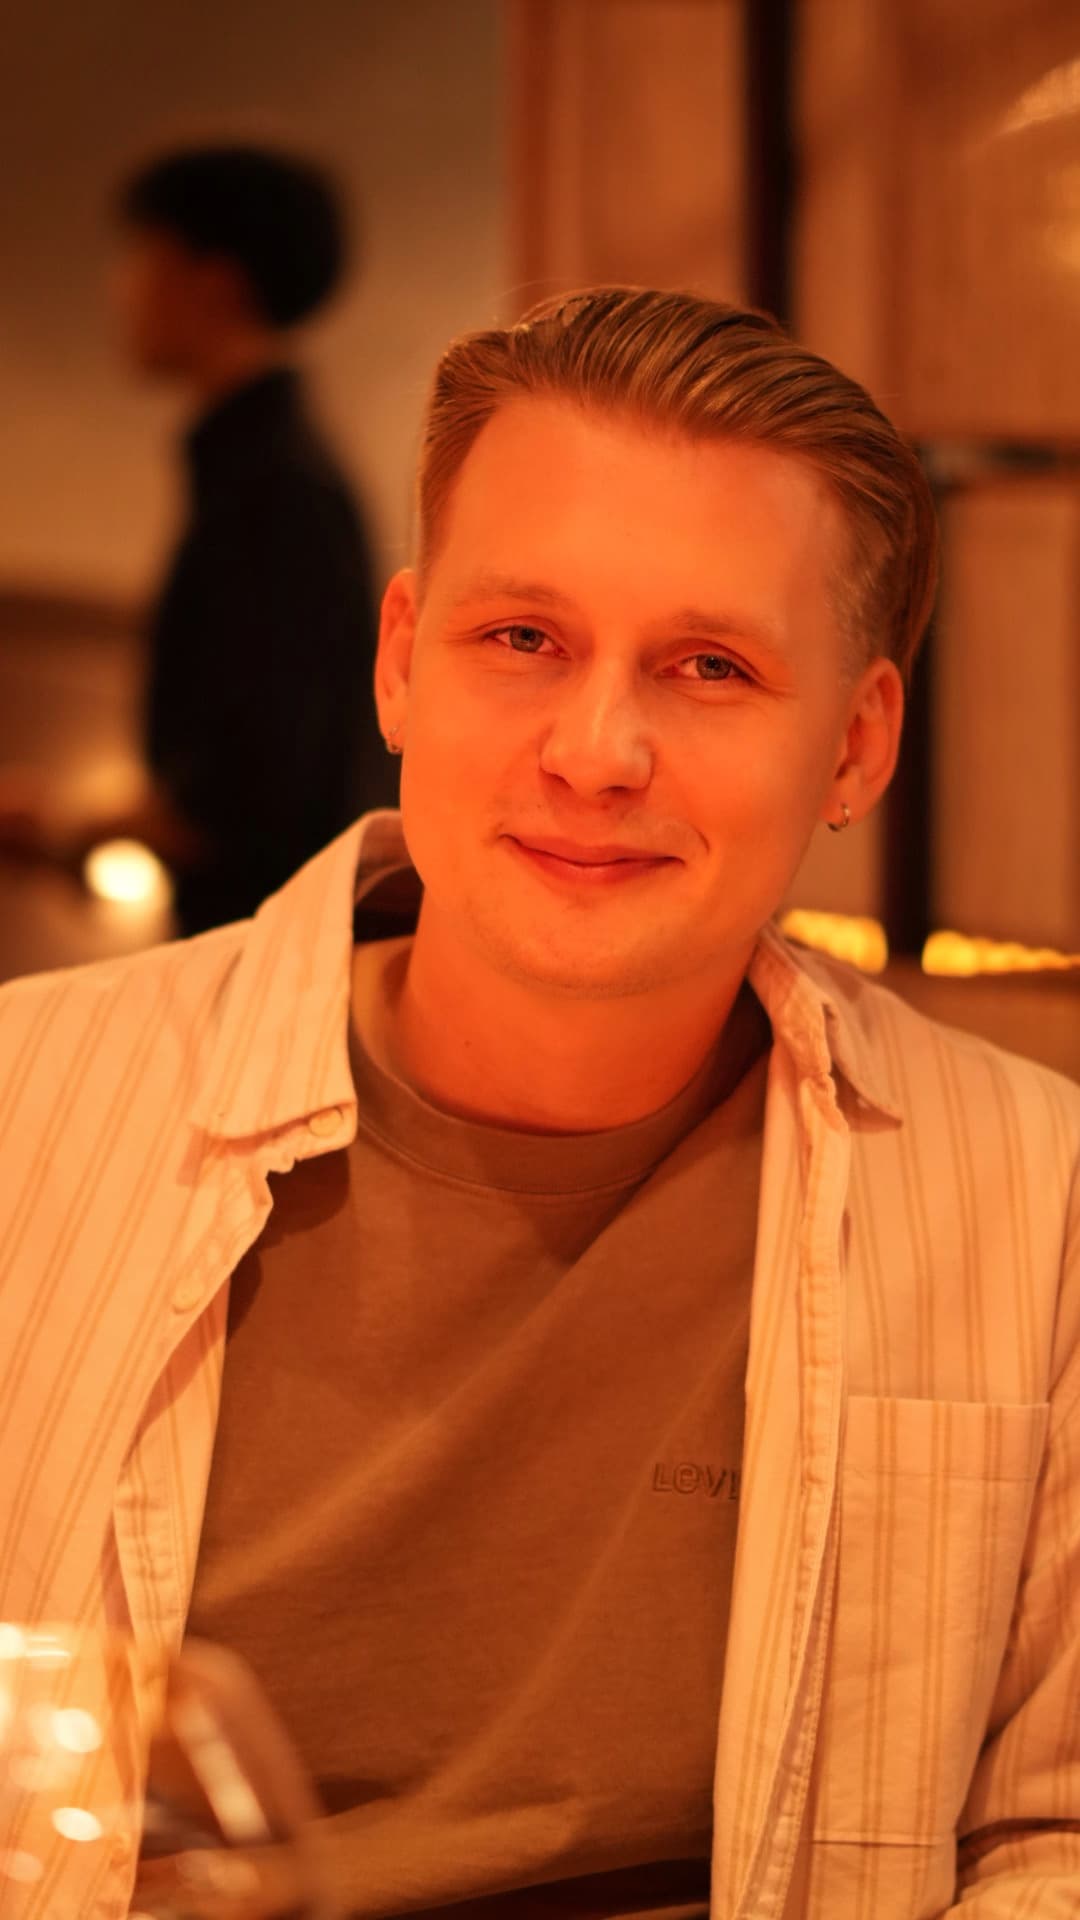
My Journey
Recently completed a Red Team Security Internship at Cloudflare, where I ran red team engagements against external and internal systems, documented attack paths, and delivered remediation recommendations with the SIRT (Security Incident Response Team).
In offensive security, AI isn't the question anymore - it's how you use it. AI compresses the grind without cutting corners. The hours that go into mapping attack surface and building PoCs - models chew through that in minutes. You see it everywhere now: internal AI tools for PoC generation, and Burp AI shipping it commercially. What does not compress is judgement: which finding actually threatens the business, chaining three mediums into one that ends the engagement, and recognising when the model is confidently wrong. The same models are now the target. An LLM application is an attack surface with its own failure modes: prompt injection through content the model reads, jailbreaks that walk past the system prompt, data pulled out through the model or the tools it can call, and poisoned data that quietly changes what it does. I test those the same way I test a web app, against the OWASP Top 10 for LLM Applications, with a proof of concept for every finding.
Delivered a full web application and REST API assessment for a UK organisation on my own schedule, scoping through report: OWASP methodology, CVSS scored findings, and fixes the client could actually implement. Assessed an LLM agent for what data it could reach and what tools it could call, then showed how crafted input could make it misuse them. Built my own C2 framework in Go and an AI-assisted testing harness with custom prompts and tooling. Placed 3rd at AI Odyssey 2026 in London. I read disclosed reports on HackerOne to see how other people found the bug and what they had to chain it with.
Skills & Expertise
Offensive Security Core Competencies
- Web Application & API Testing: Full engagement end to end, from scoping through testing to a delivered report, on my own schedule
- AI Security Testing: Prompt injection, jailbreaks, data exfiltration through models and tool calls, data poisoning, agent permission scoping
- Network Testing & Adversary Simulation: Reconnaissance through exploitation and post-exploitation against external and internal infrastructure
- Tooling & C2 Development: Built my own command and control framework rather than reaching for an off-the-shelf one
- AI-Assisted Testing: Compressing recon, code review and PoC work with models, and knowing where their output stops being trustworthy
- Methodology & Reporting: OWASP, PTES, CVSS severity ratings, evidence and remediation the client can act on
Technical Skills & Tools
- Offensive Tooling: Burp Suite and Burp AI, Metasploit, Nmap, Kali Linux, Wireshark, own C2 framework in Go
- AI Tooling: OWASP Top 10 for LLM Applications, opencode with model APIs, custom prompts and tooling, MCP endpoint testing
- Web & API: OWASP Top 10, injection, broken authentication and access control, IDOR, REST API testing
- Programming: Go, Python, Bash, PowerShell, SQL, Node.js
- Networks & Systems: TCP/IP, firewalls, segmentation, Linux and Windows privilege escalation, Docker, AWS, Azure
- Frameworks: OWASP, PTES, MITRE ATT&CK, CVSS
Experience
Red Team Security Intern
Cloudflare
London, UK
JUN 2026 – SEP 2026
4 months
Cyber Lab Assistant
University of Roehampton
London, UK
OCT 2025 – MAY 2026
7 months
Co-Founder & Operations Director
Model Agency
Ukraine / Remote
AUG 2021 – AUG 2023
2 years
Cadet to Fourth Engineer
Stolt Tankers
Worldwide (sea)
DEC 2019 – JUN 2021
1 year 6 months
Education
BSc Cyber Security
University of Roehampton
London, UK
Grade: First Class Honours
Marine Engineer
National University "Odessa Maritime Academy"
Odessa, Ukraine
First Class Honours
Articles
Sharing my insights, projects, thoughts, and experiences
My Red Team Internship at Cloudflare: The Story So Far
A few months into a Red Team Security Internship at Cloudflare. Attacking production infrastructure, then working with the blue team to detect and fix what I found. On scale, building my own C2, and my first physical pentest.
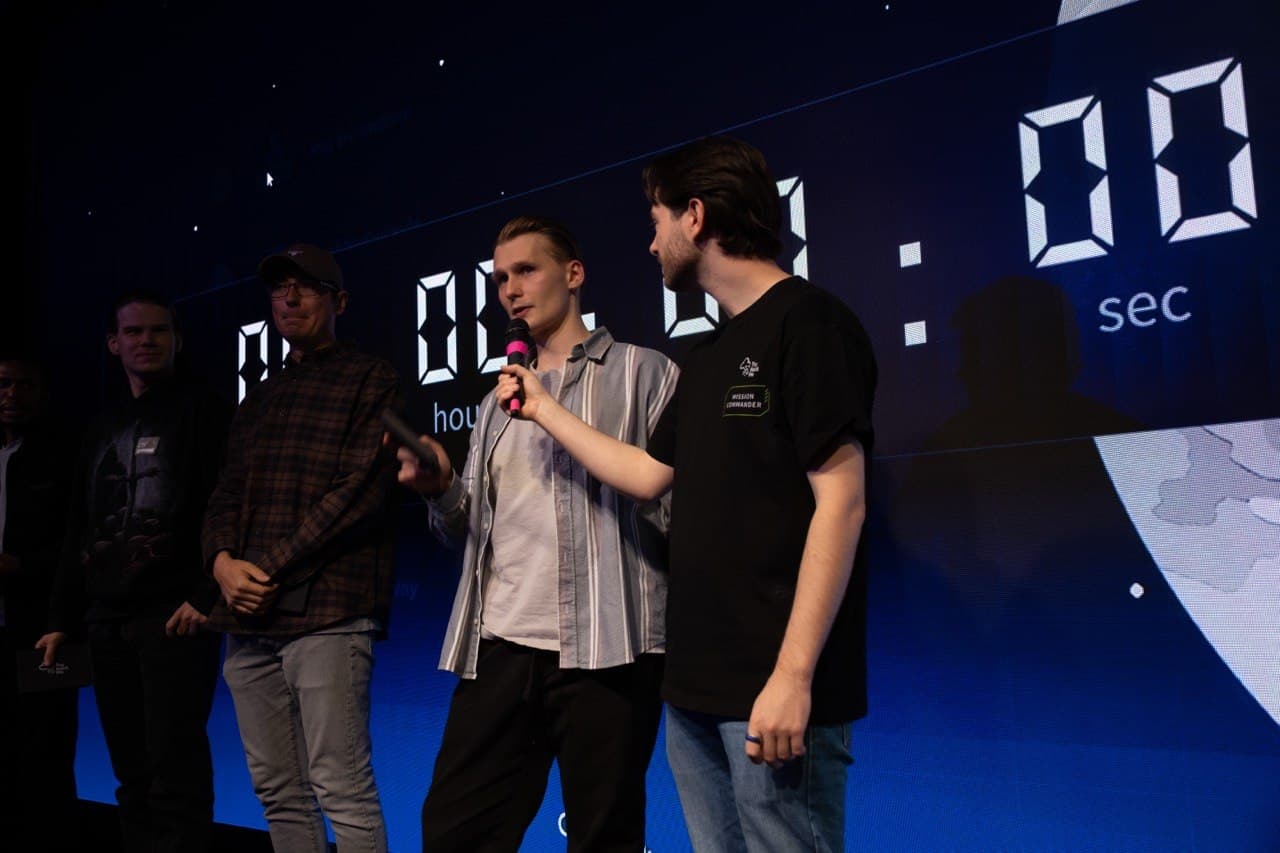
How We Placed 3rd at the London AI Odyssey CTF 2026
Teaming up with strangers from different countries and backgrounds at the AI Odyssey CTF 2026 in London, and walking away with a 3rd-place finish.
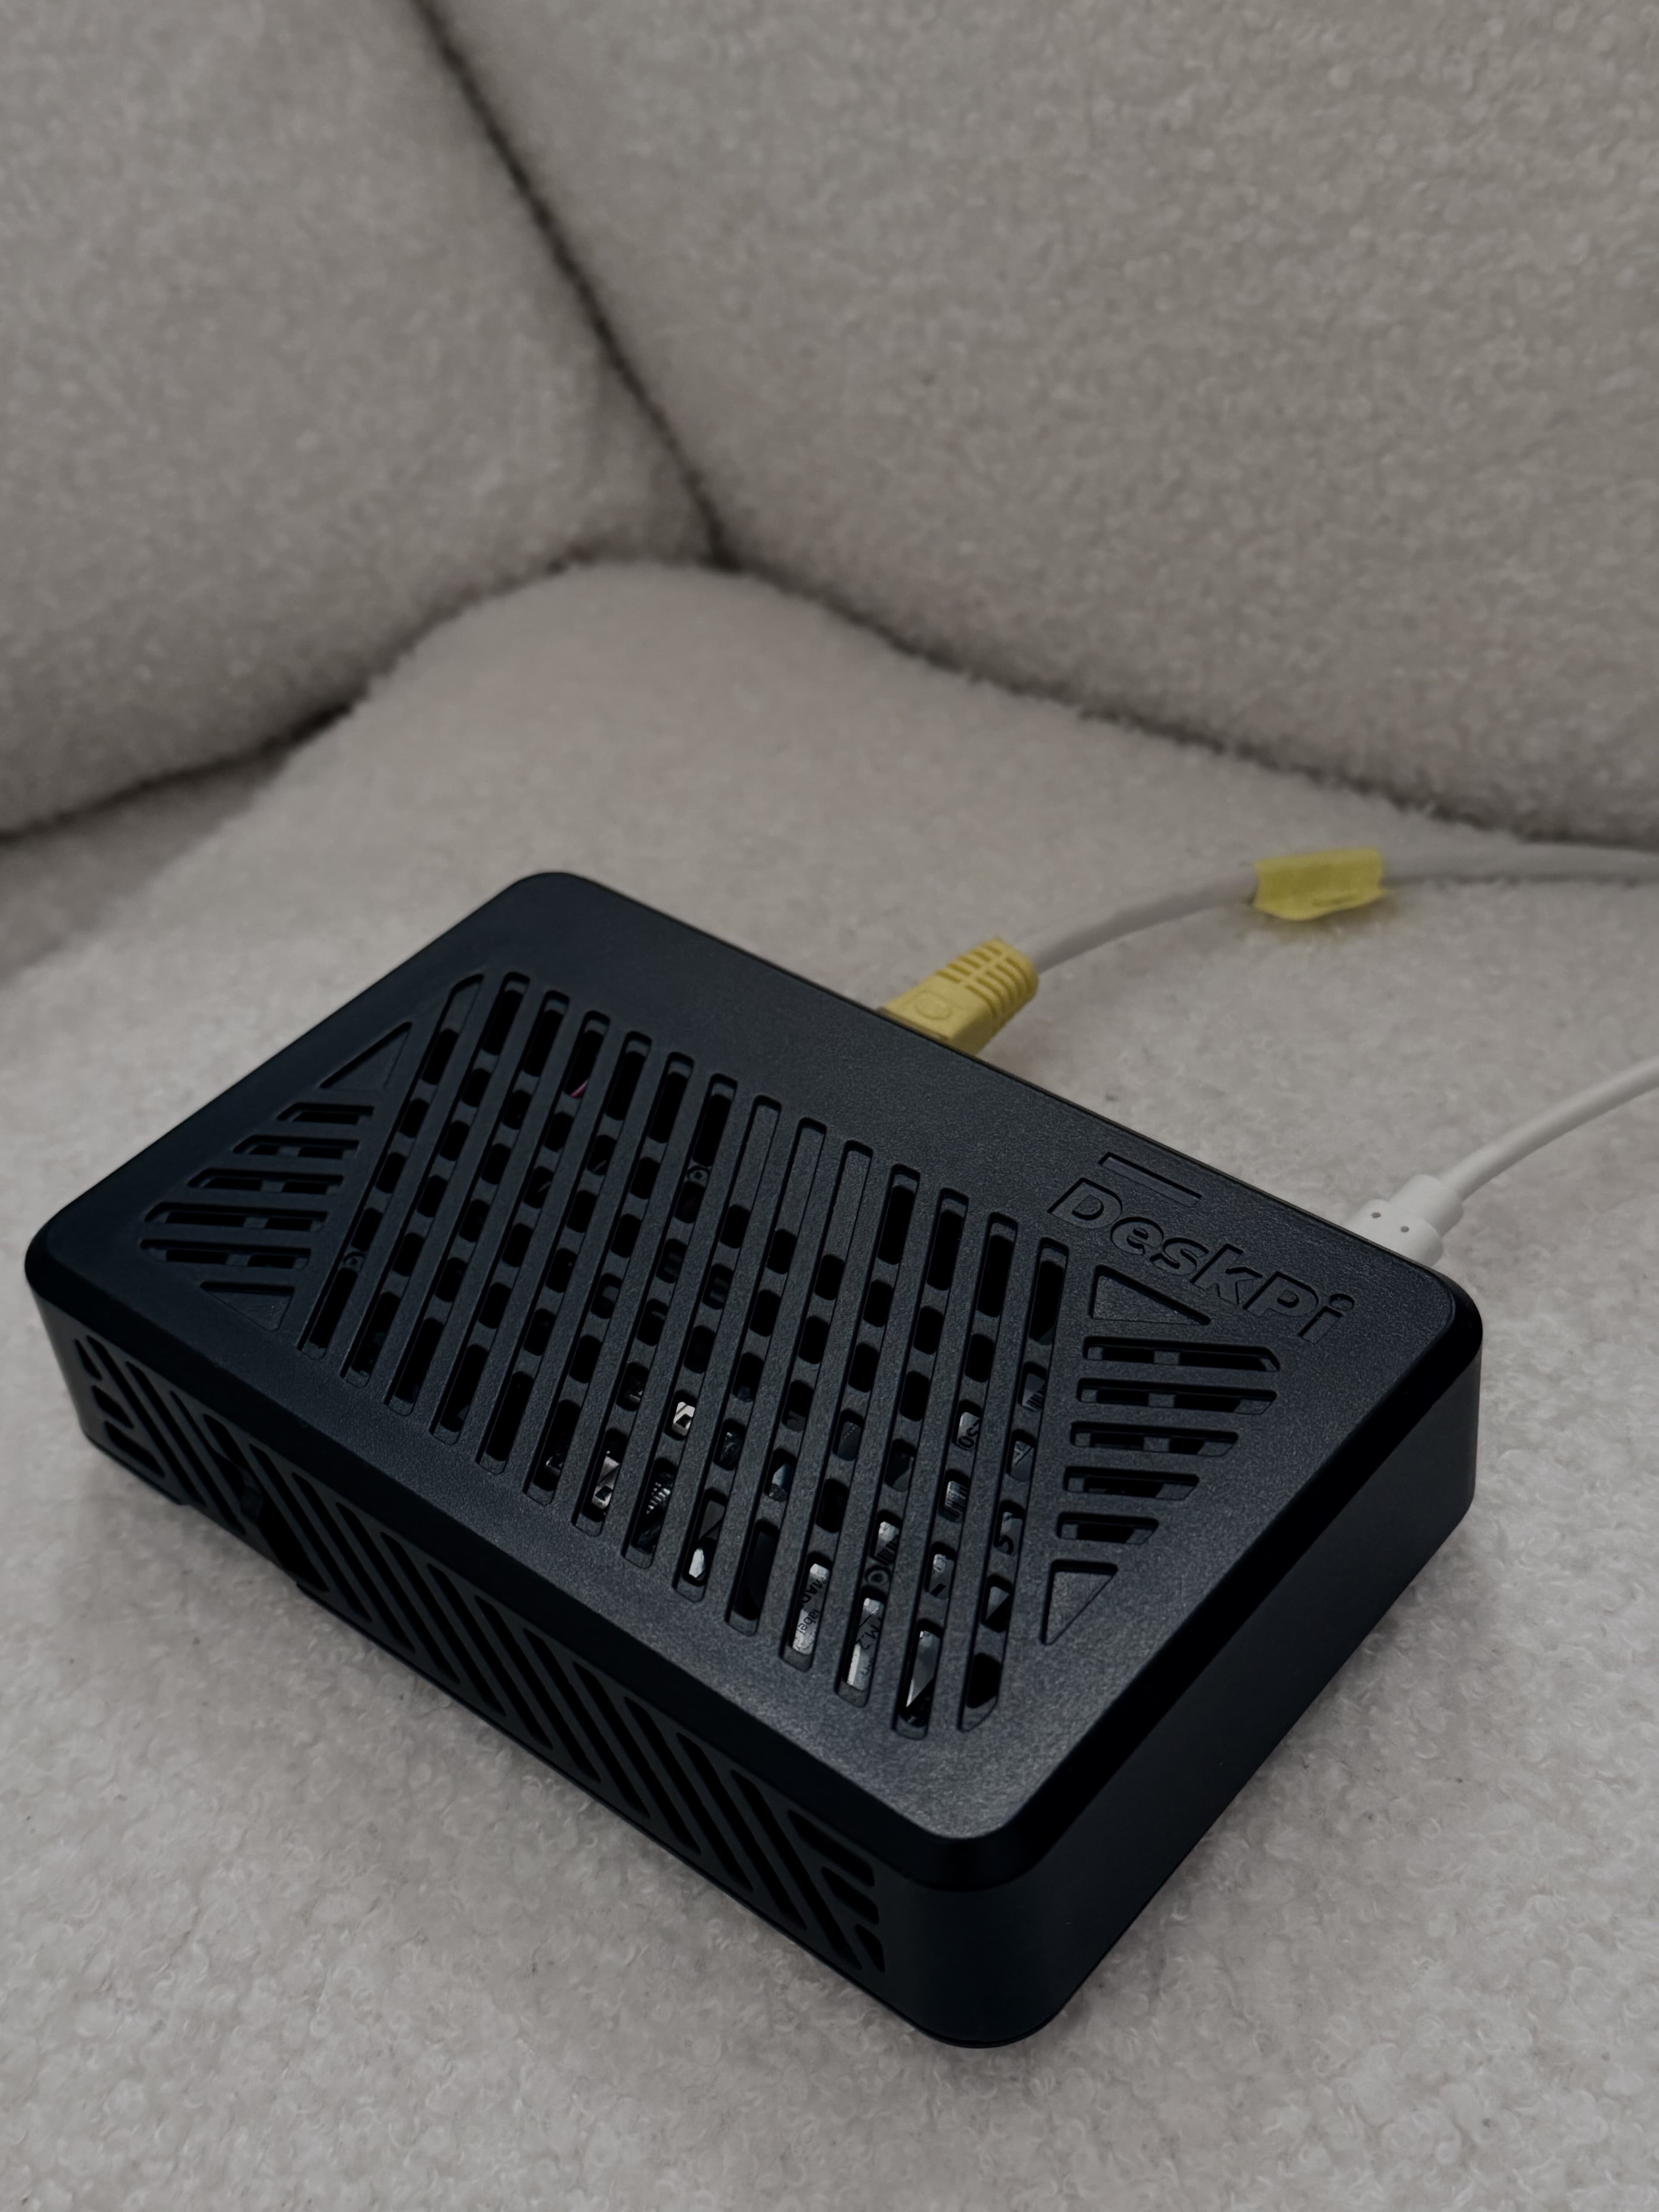
Deploying my own website on a home server
Step-by-step guide to self-hosting a Next.js site on a Raspberry Pi with Nginx, SSL, and systemd. Learn how I deployed my portfolio on a £35 home server instead of paying for cloud hosting.
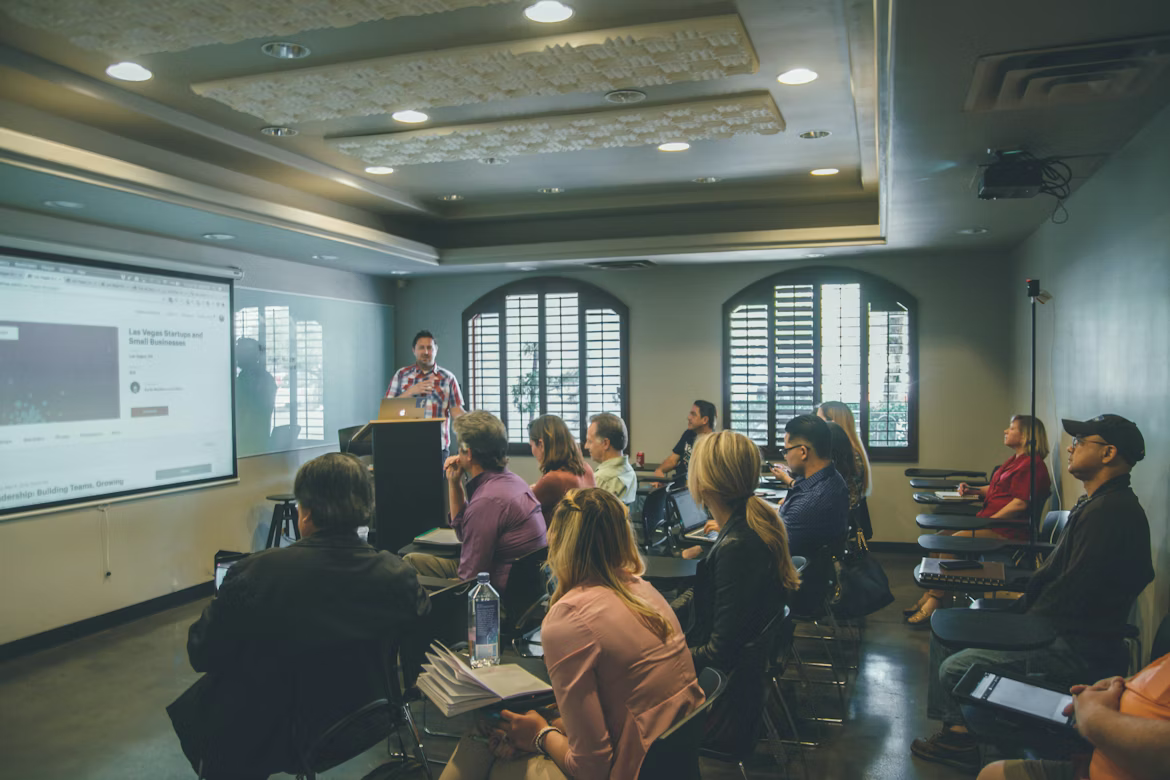
Supporting students as a computer lab assistant
How teaching network security and penetration testing to university students sharpened my ability to explain complex technical concepts to diverse audiences - essential skills for cybersecurity analysts who must communicate security decisions and act as ambassadors of security best practices.
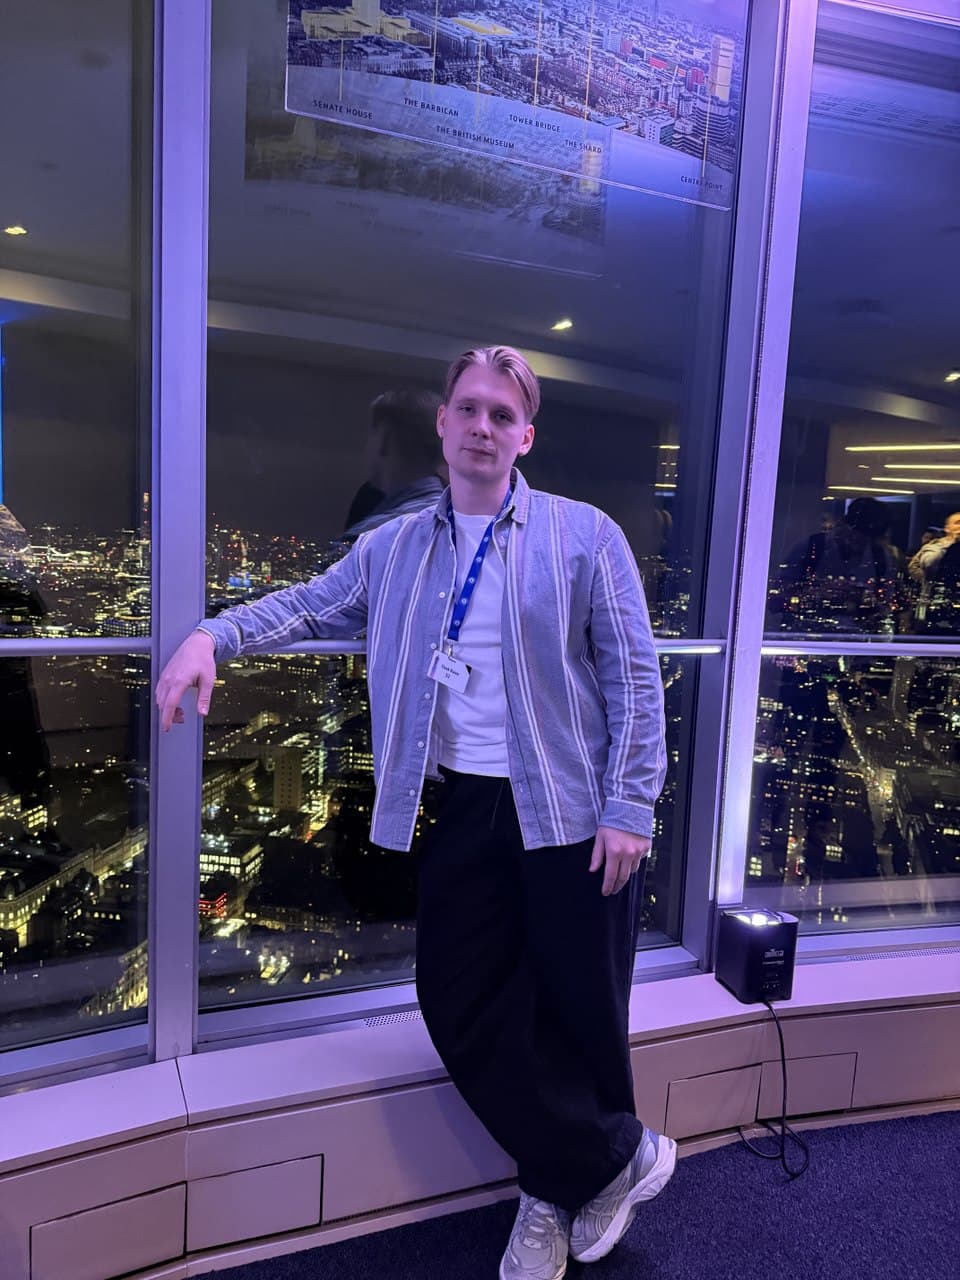
Competing at the UK Cyber Leaders Challenge
A national incident response exercise: a cyberattack on two UK ports, a containment strategy built from partial intelligence, and ten minutes defending it under questioning from government and industry judges.
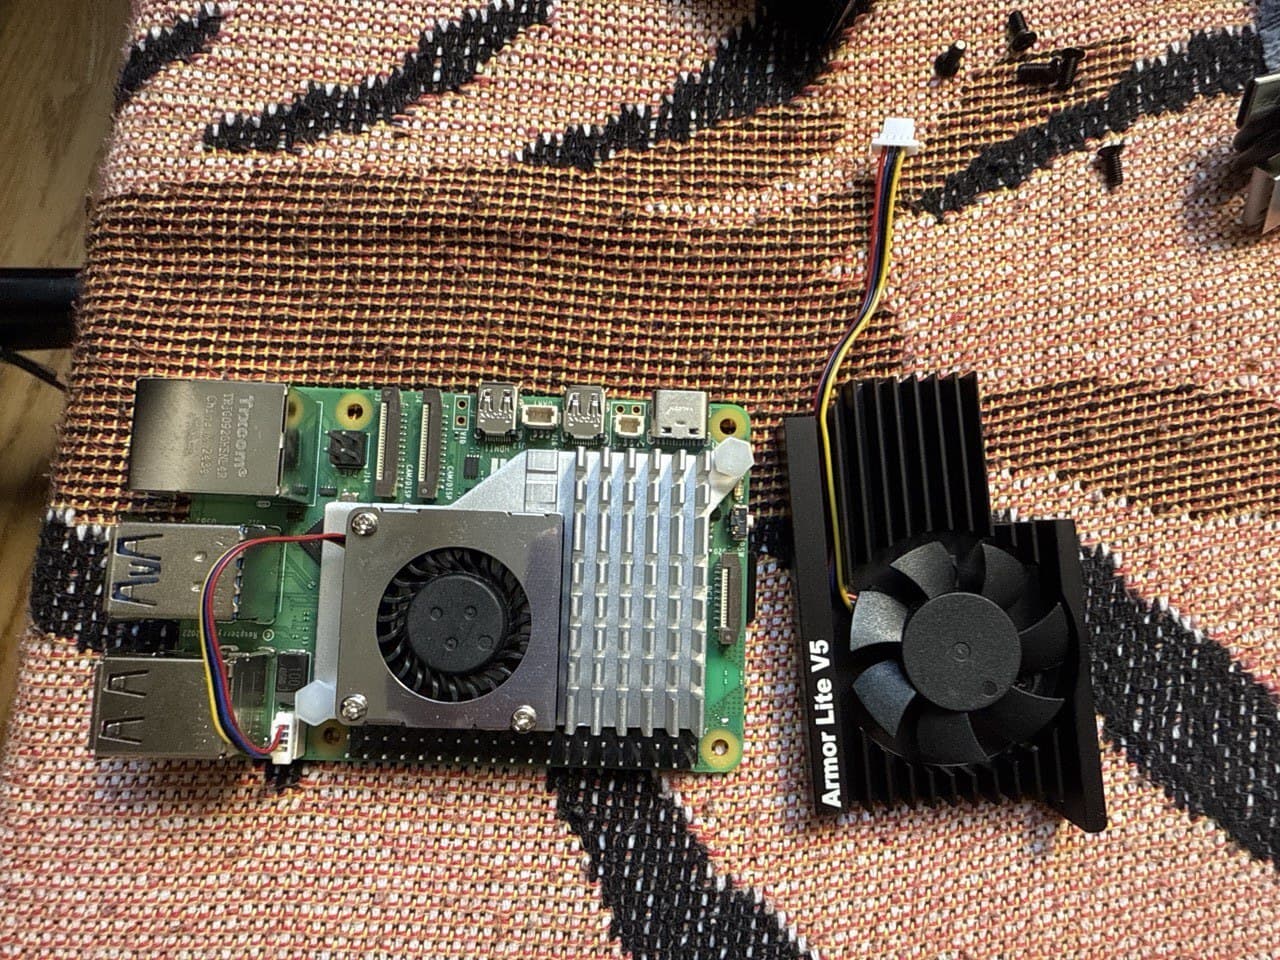
Installing Arch Linux on Raspberry Pi 5 and fixing HDMI issues
Installing Arch Linux on Raspberry Pi 5 isn't officially supported yet. Here's how I worked around U-Boot incompatibilities and fixed the HDMI display issue that left me with a booting system but no video output.
Achievements
Regional Math Olympiad Winner
1st Place
Achieved first place in the Regional Mathematics Olympiad, Odessa region, Ukraine. Demonstrated exceptional analytical thinking and problem-solving capabilities in competitive mathematics.
Regional IT Olympiad Winner
2nd Place
Secured second place in the Regional IT Olympiad, Odessa region, Ukraine. Showcased strong technical aptitude and computational thinking in competitive programming and computer science.
BSc Cyber Security
University of Roehampton
Graduated with a BSc in Cyber Security, demonstrating comprehensive understanding of security principles, threat analysis, and defensive strategies.
EJPT Certification
Junior Penetration Tester
Earned eLearnSecurity Junior Penetration Tester certification, validating practical skills in penetration testing, vulnerability assessment, and ethical hacking methodologies.
Certification ID: 140964497
Cyber Security Society
Founder & President (2023–2026)
Founded and led the Cyber Security Society at University of Roehampton, growing it to 30+ active members. Organized weekly sessions on penetration testing, security research, and knowledge sharing until handing over leadership upon graduating in 2026.
UK Cyber Leaders Challenge
Participant
Selected participant in the UK Cyber Leaders Challenge 2025, Cheltenham. Engaged in scenario-based competitions involving critical infrastructure breaches and strategic response planning from a government perspective.
Capture The Flag Winner
Multiple Victories
1st Place: Roehampton CTF
1st Place: Sheffield Siege CTF
2nd Place: HackTheBox CTF
3rd Place: AI Odyssey 2026, London
Consistently ranked at the top in competitive cybersecurity challenges, demonstrating advanced skills in penetration testing, reverse engineering, and exploit development.
Advanced Projects
Cybersecurity & Infrastructure
Developed multiple sophisticated security projects including business infrastructure assessment using ELK + Wazuh log analysis aligned with ISO 27001 and NIST CSF frameworks, a secure Node.js/Express + MySQL web application for penetration testing with SQLi, XSS, and CSRF vulnerability mitigation, and bootloader exploit analysis with bootkit identification and GPT integrity recovery.
Karate Practitioner
2nd Brown Belt (2nd Kyu)
Practiced karate for over 12 years, beginning in childhood and continuing with Chelsea Karate Club in London. Achieved second brown belt (one rank before black belt).
Contact
I'm always open to discussing opportunities, collaborations, research projects, or answering questions. Feel free to reach out if you'd like to connect.