Articles
Sharing my insights, projects, thoughts, and experiences
My Red Team Internship at Cloudflare: The Story So Far
A few months into a Red Team Security Internship at Cloudflare. Attacking production infrastructure, then working with the blue team to detect and fix what I found. On scale, building my own C2, and my first physical pentest.
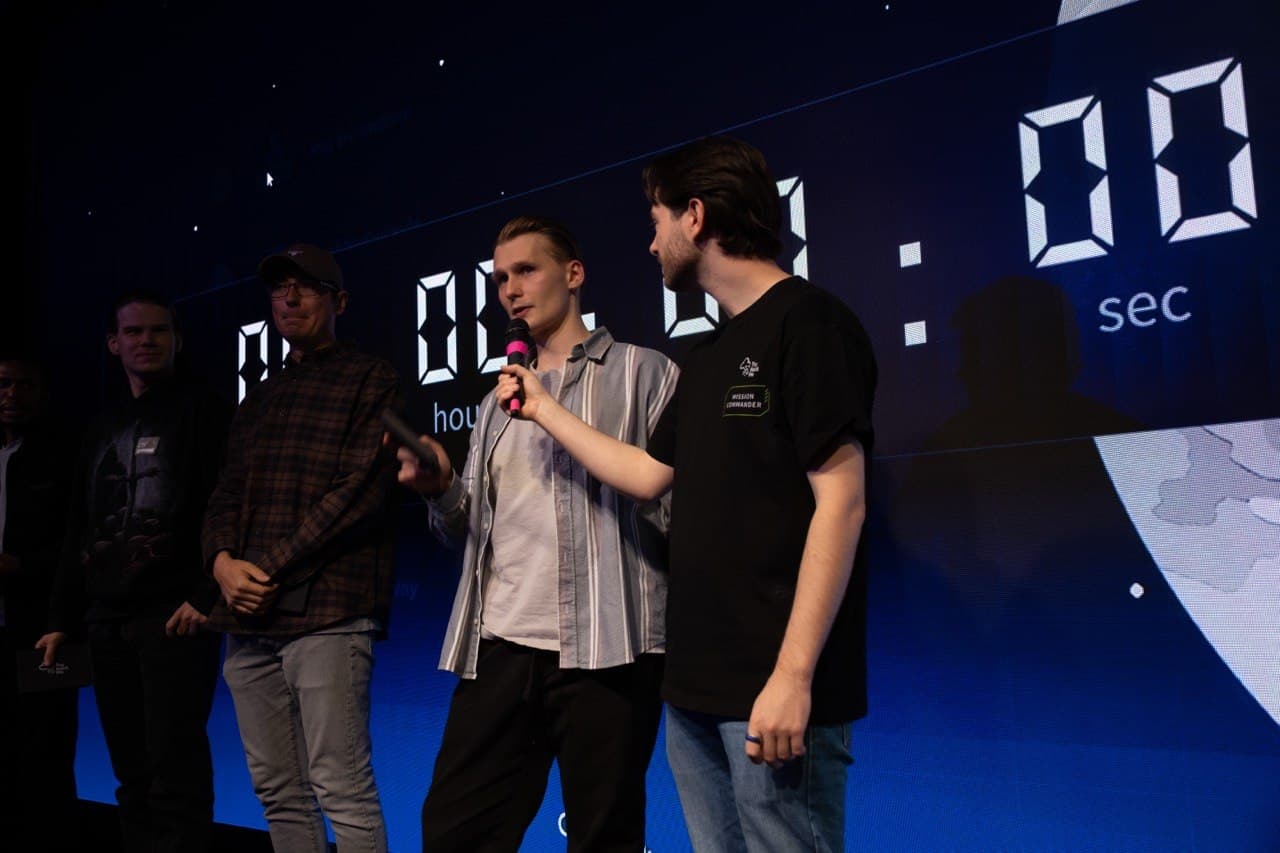
How We Placed 3rd at the London AI Odyssey CTF 2026
Teaming up with strangers from different countries and backgrounds at the AI Odyssey CTF 2026 in London, and walking away with a 3rd-place finish.
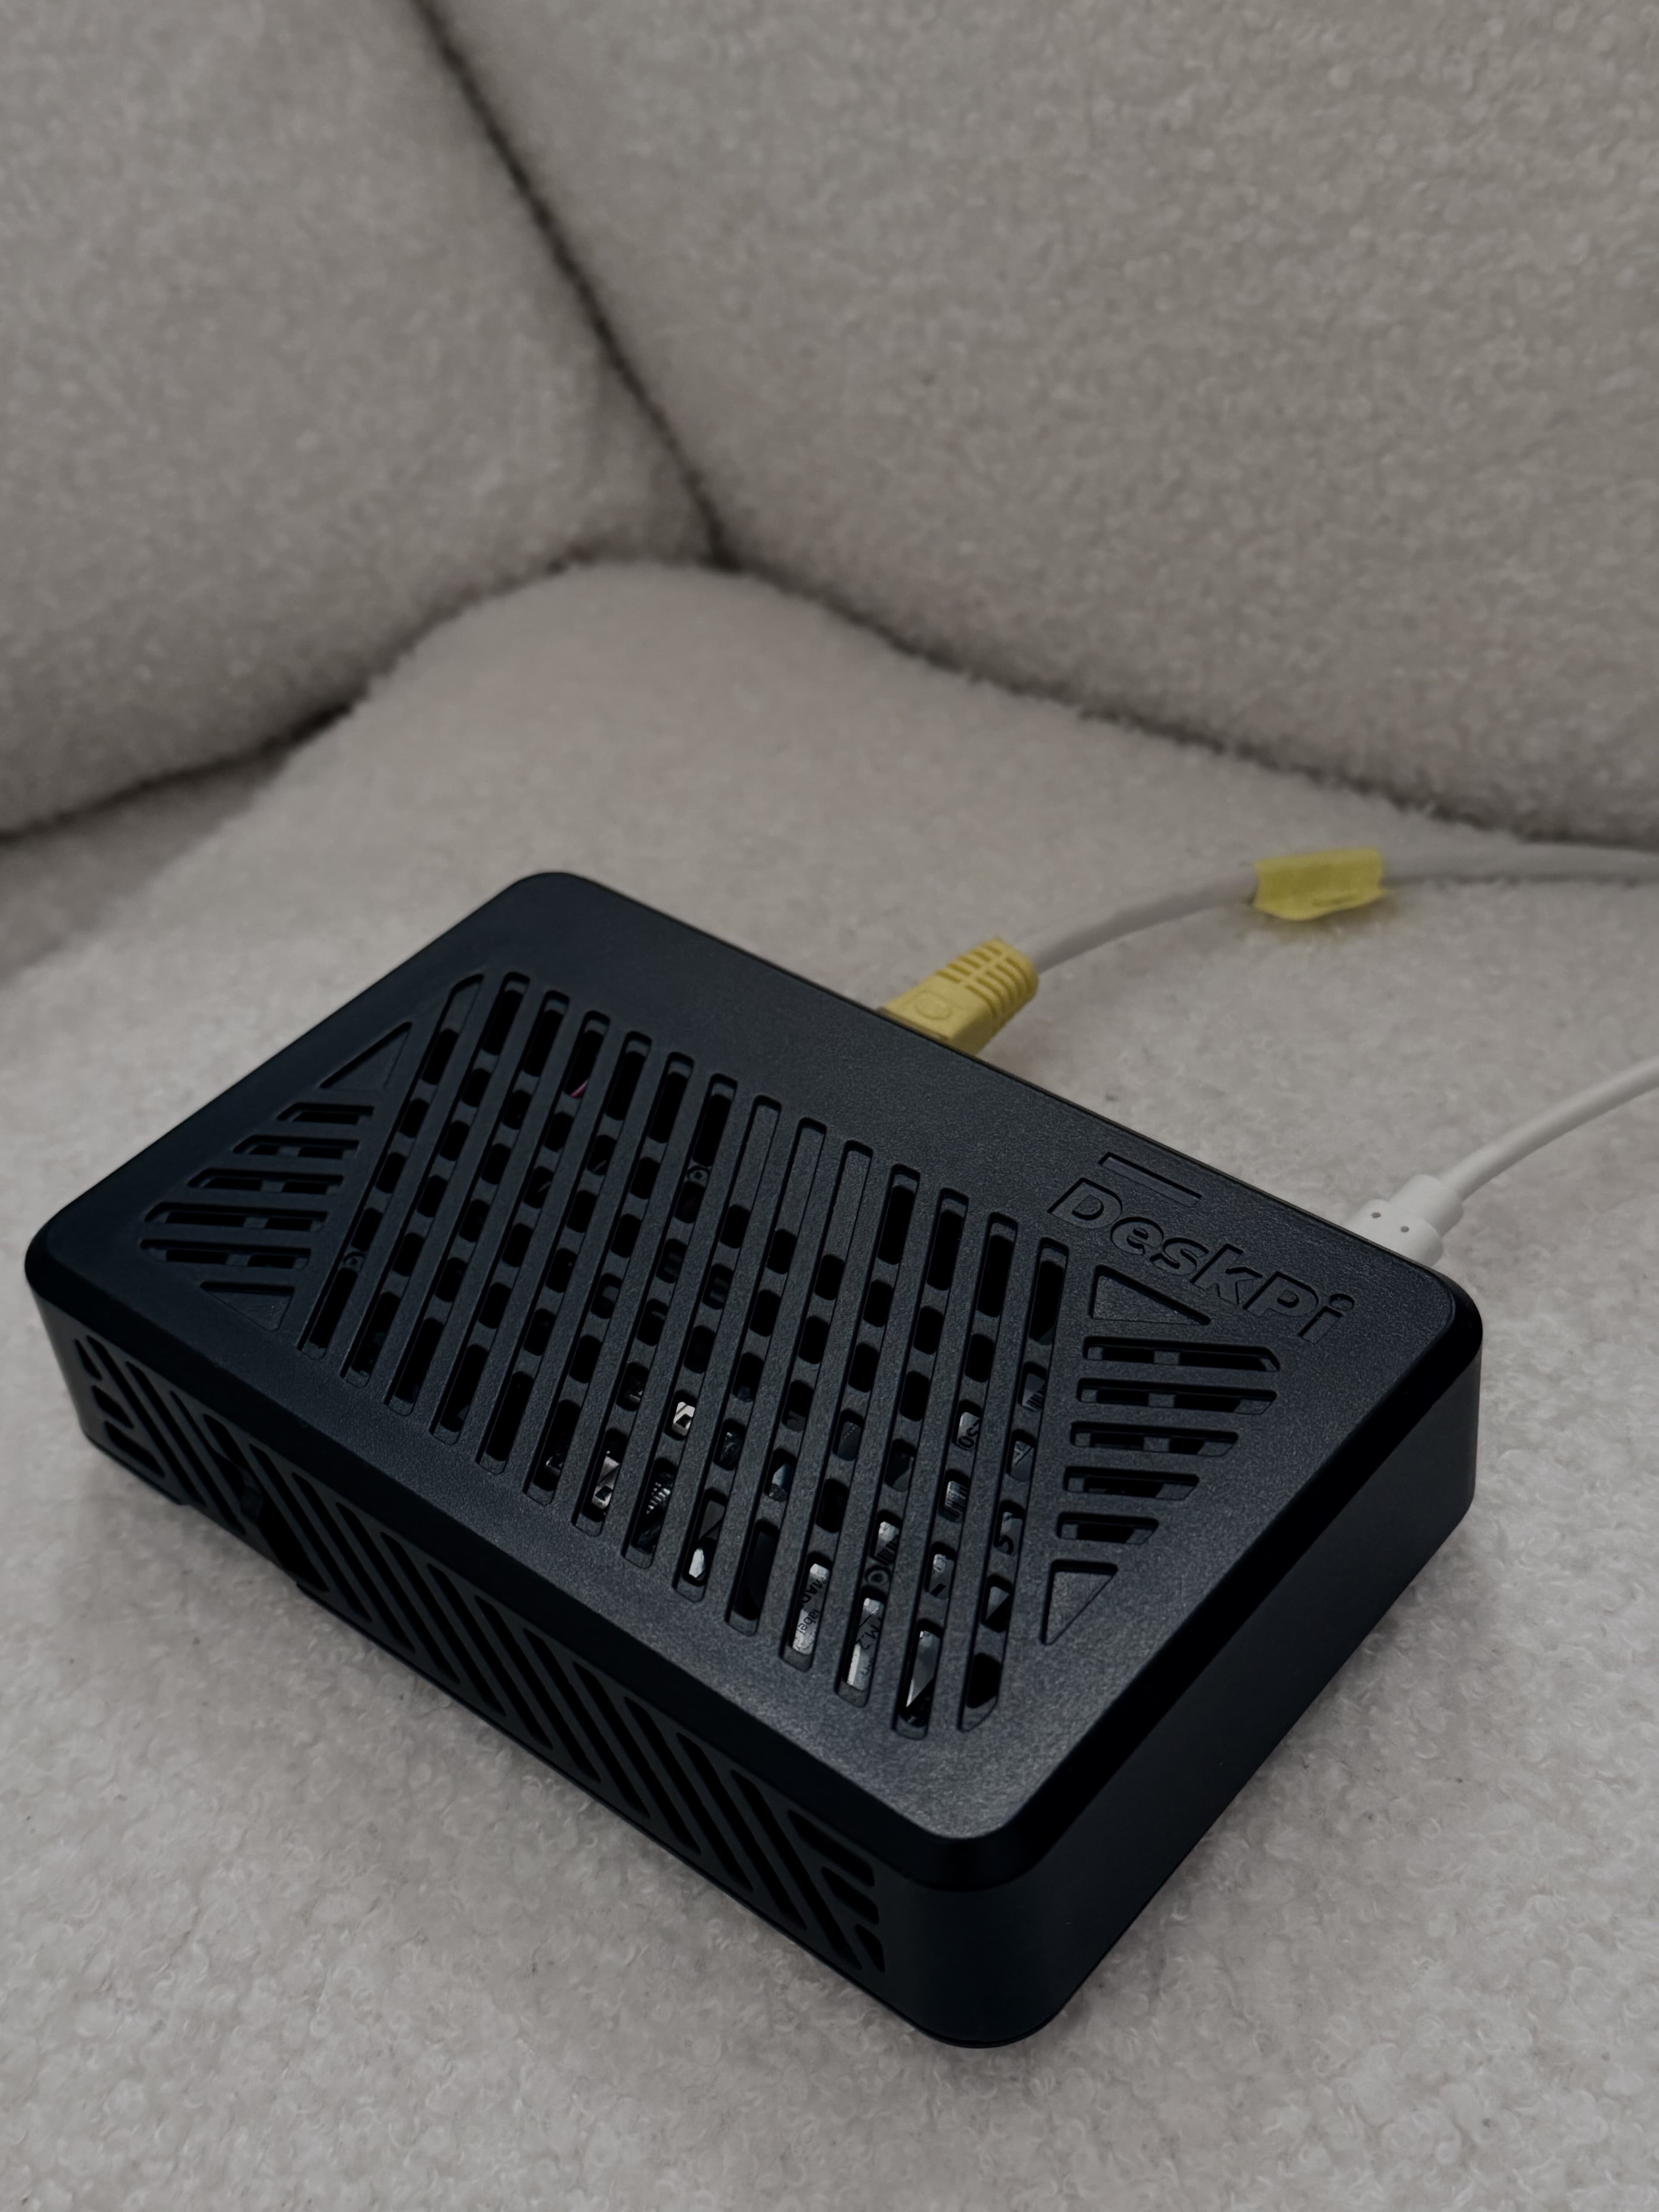
Deploying my own website on a home server
Step-by-step guide to self-hosting a Next.js site on a Raspberry Pi with Nginx, SSL, and systemd. Learn how I deployed my portfolio on a £35 home server instead of paying for cloud hosting.
Supporting students as a computer lab assistant
How teaching network security and penetration testing to university students sharpened my ability to explain complex technical concepts to diverse audiences - essential skills for cybersecurity analysts who must communicate security decisions and act as ambassadors of security best practices.
Competing at the UK Cyber Leaders Challenge
A national incident response exercise: a cyberattack on two UK ports, a containment strategy built from partial intelligence, and ten minutes defending it under questioning from government and industry judges.
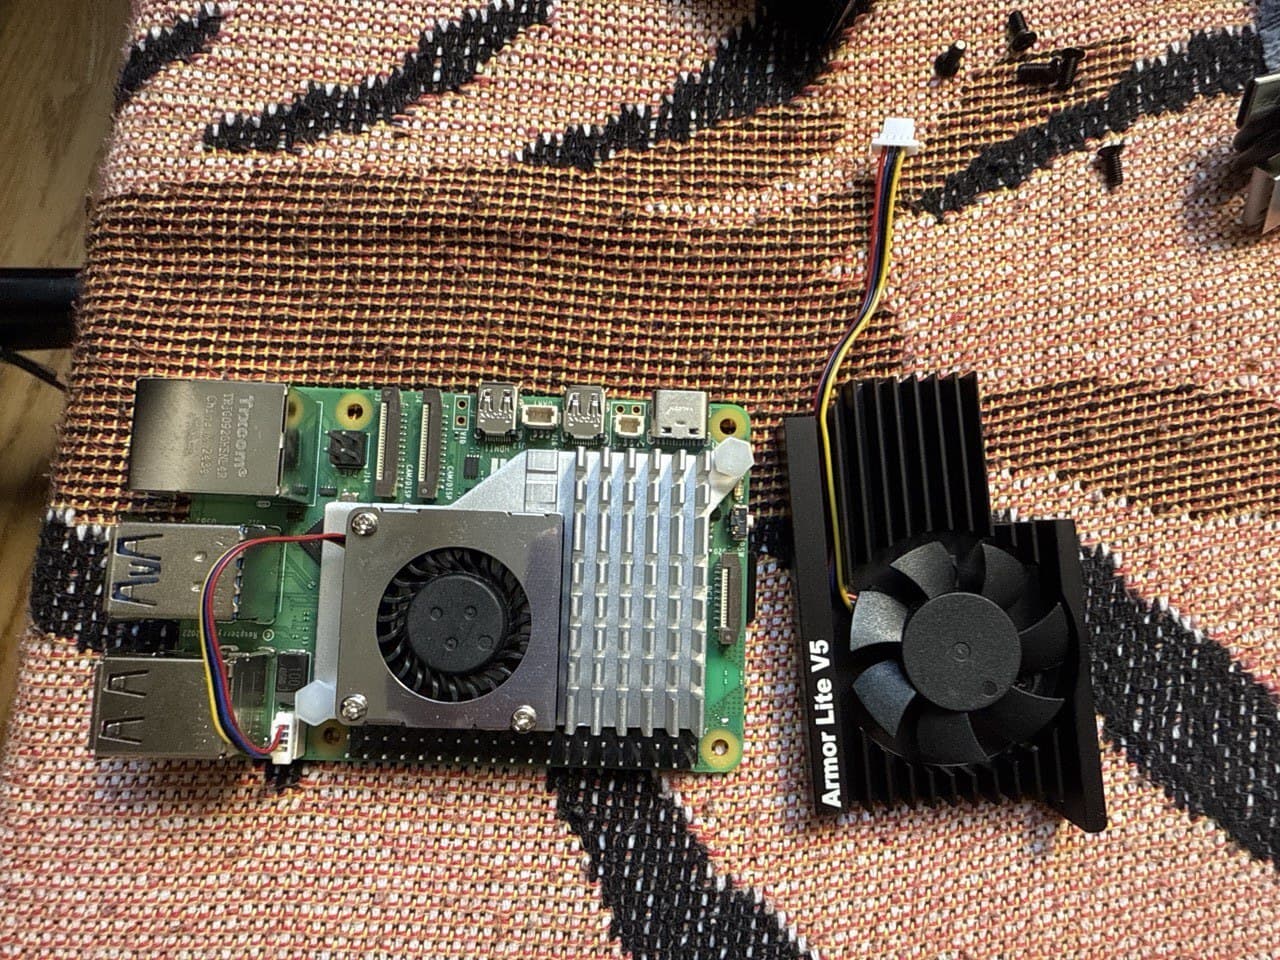
Installing Arch Linux on Raspberry Pi 5 and fixing HDMI issues
Installing Arch Linux on Raspberry Pi 5 isn't officially supported yet. Here's how I worked around U-Boot incompatibilities and fixed the HDMI display issue that left me with a booting system but no video output.
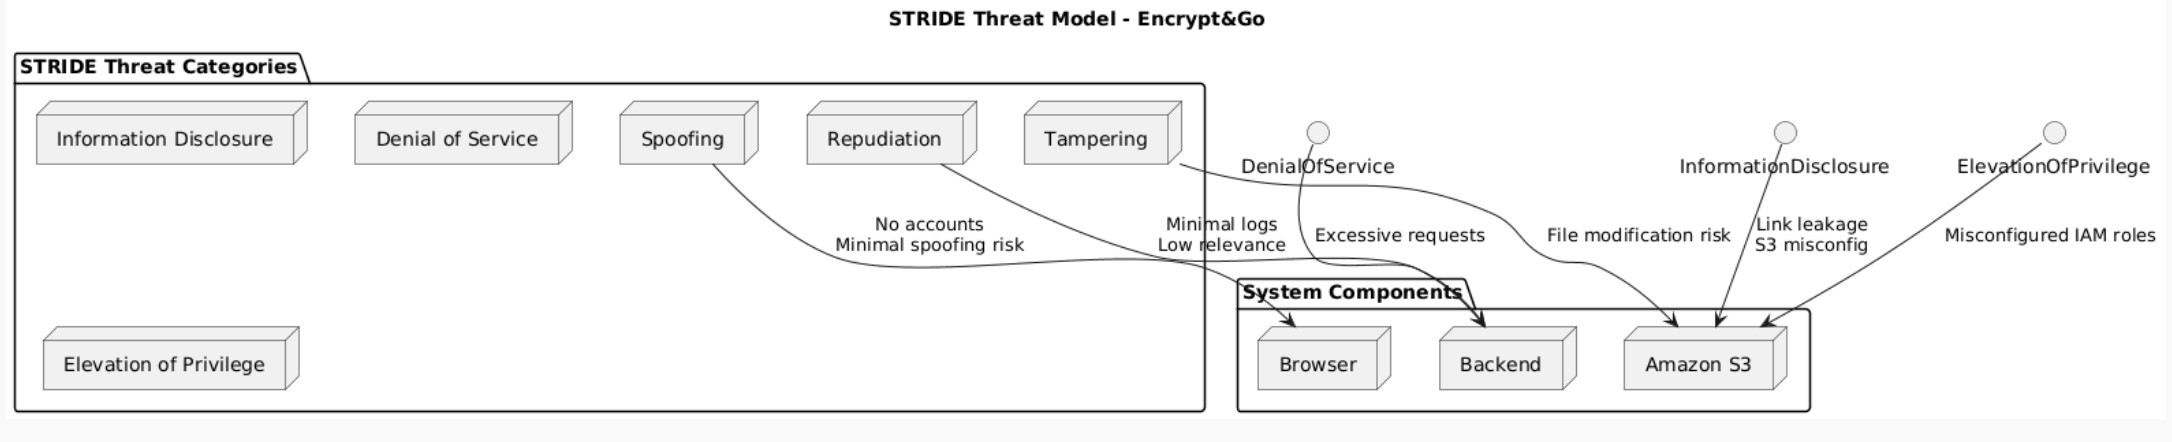
Building secure systems through threat modeling
A comprehensive guide to threat modeling using the STRIDE framework, with a practical case study of Encrypt&Go - a secure file encryption and sharing system. Learn how to identify threats, assess risks, and design secure architectures.
AML detection in blockchain systems
My final-year project building an ML-powered AML detection system for blockchain networks. Developed algorithms to identify money laundering patterns across Ethereum and TRON transactions.
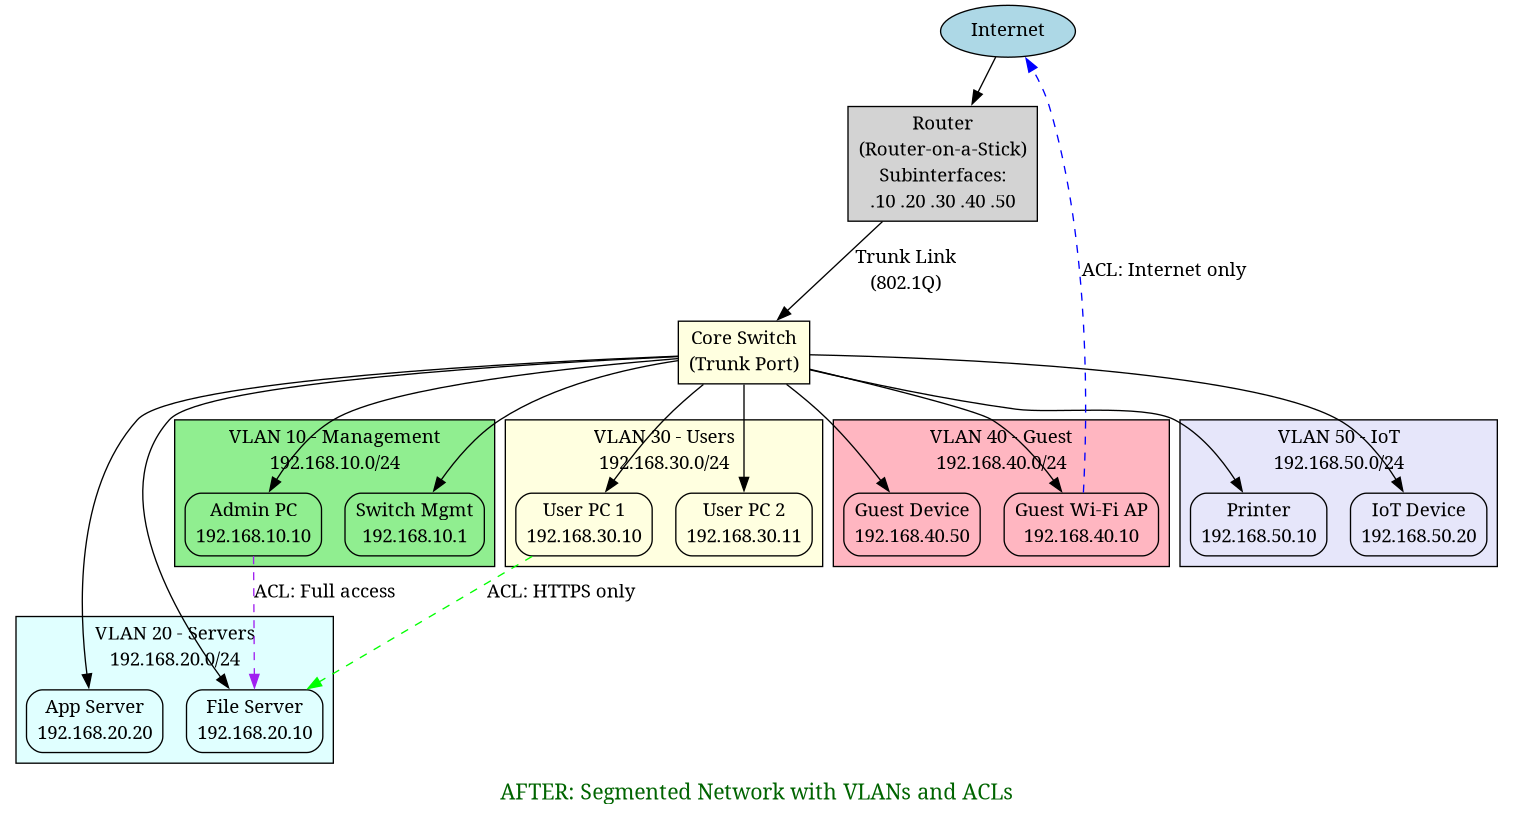
Network segmentation with VLANs to limit lateral movement
Redesigned a flat network into segmented VLANs to stop attackers from moving laterally. Used router-on-a-stick and ACLs to isolate users, servers, guests, and IoT devices - turning a compromised workstation into a contained threat.
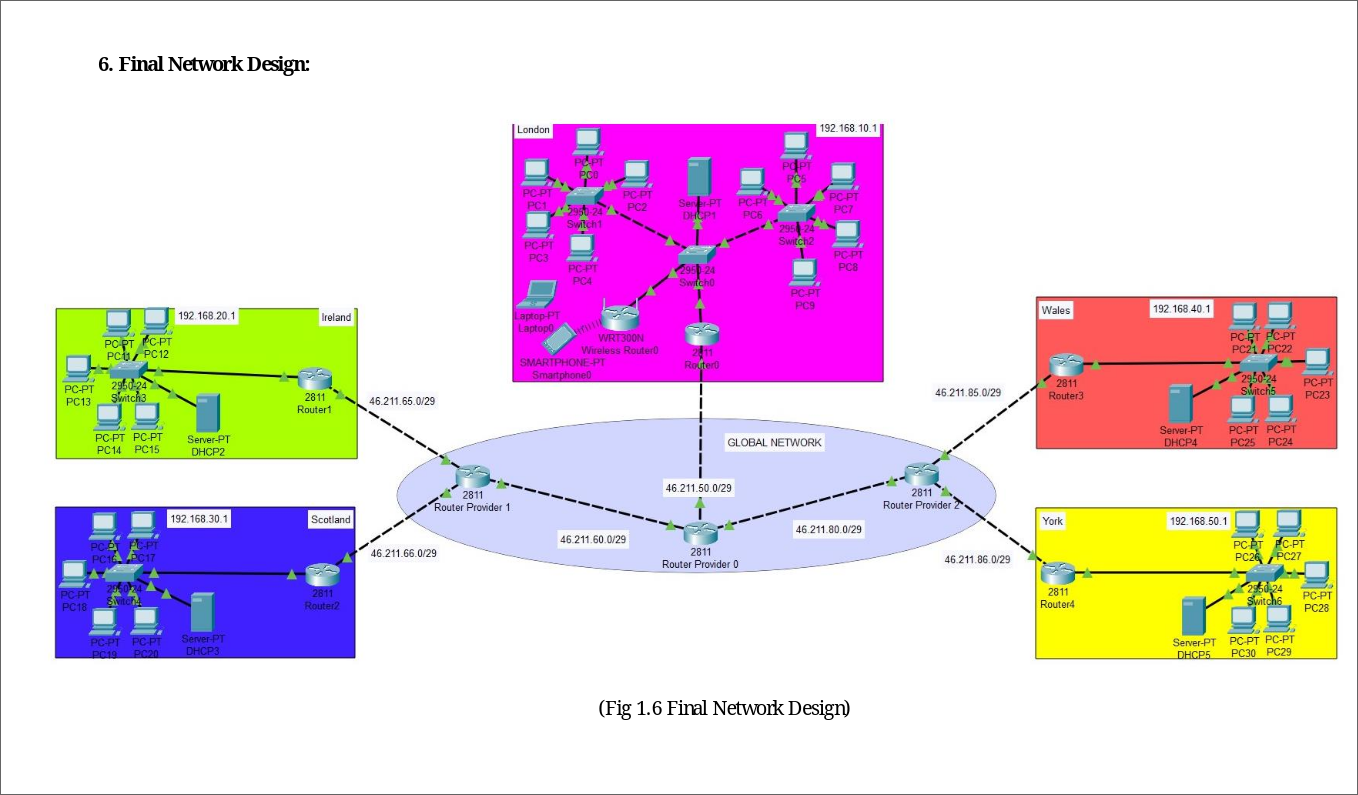
Designing a network security architecture for multiple offices
Coursework project designing a multi-branch network architecture with VPN tunnels, DHCP, NAT, and security policies. Built the complete design in Cisco Packet Tracer to connect offices across the UK.
From Data to Action: Building Fraud Risk Metrics
Building fraud risk metrics that actually drive decisions. Learn how to create BCIs and KRIs that transform raw data into actionable insights for fraud prevention teams.
Synthetic identities and financial crime
Synthetic identity fraud combines real and fake information to create entirely new identities. Explore how this fast-growing financial crime works and the detection strategies used to catch it.
Acquiring Fraud: Detection and Prevention Strategies
Acquiring fraud targets merchants and payment processors directly. Learn how fraudsters exploit payment systems and the detection strategies used to protect businesses.
Analysing Fraud Patterns: A Data-Driven Approach
Using SQL, Python, and data visualization to hunt for fraud patterns. A data-driven approach to building detection models and uncovering suspicious activity.
Understanding money laundering techniques in digital banking
Exploring how money launderers exploit digital banking through fanout, layering, and mixing patterns - and the detection methods used to identify suspicious transaction flows.
The evolution of issuing fraud in fintech
How card fraud has evolved from simple skimming to sophisticated fintech attacks. Explore the changing threat landscape and modern detection strategies.
Understanding the OWASP Top 10 security risks
Understanding the OWASP Top 10 - the most critical web application security risks every developer should know, from injection attacks to broken authentication.
Getting started with penetration testing
A beginner-friendly introduction to penetration testing, covering the fundamentals, essential tools, and how to get started with ethical hacking.
Presenting penetration testing findings to non-technical clients
Security Testing coursework where I performed a penetration test and learned to present technical vulnerabilities to non-technical stakeholders using analogies and business impact - essential skills for cybersecurity analysts explaining security decisions and incident findings.

Building a network scanner tool
Building a Python network scanner tool for security assessments, featuring port scanning, service detection, and vulnerability assessment capabilities.

Web application security audit framework
A practical framework for conducting security audits of web applications, covering methodology, tools, and best practices for identifying vulnerabilities.